Government data security protocols, regulatory compliance mechanisms, and inter-agency cybersecurity oversight are confronting heightened examination as authorities launch investigative procedures into reported data compromises across state platforms.
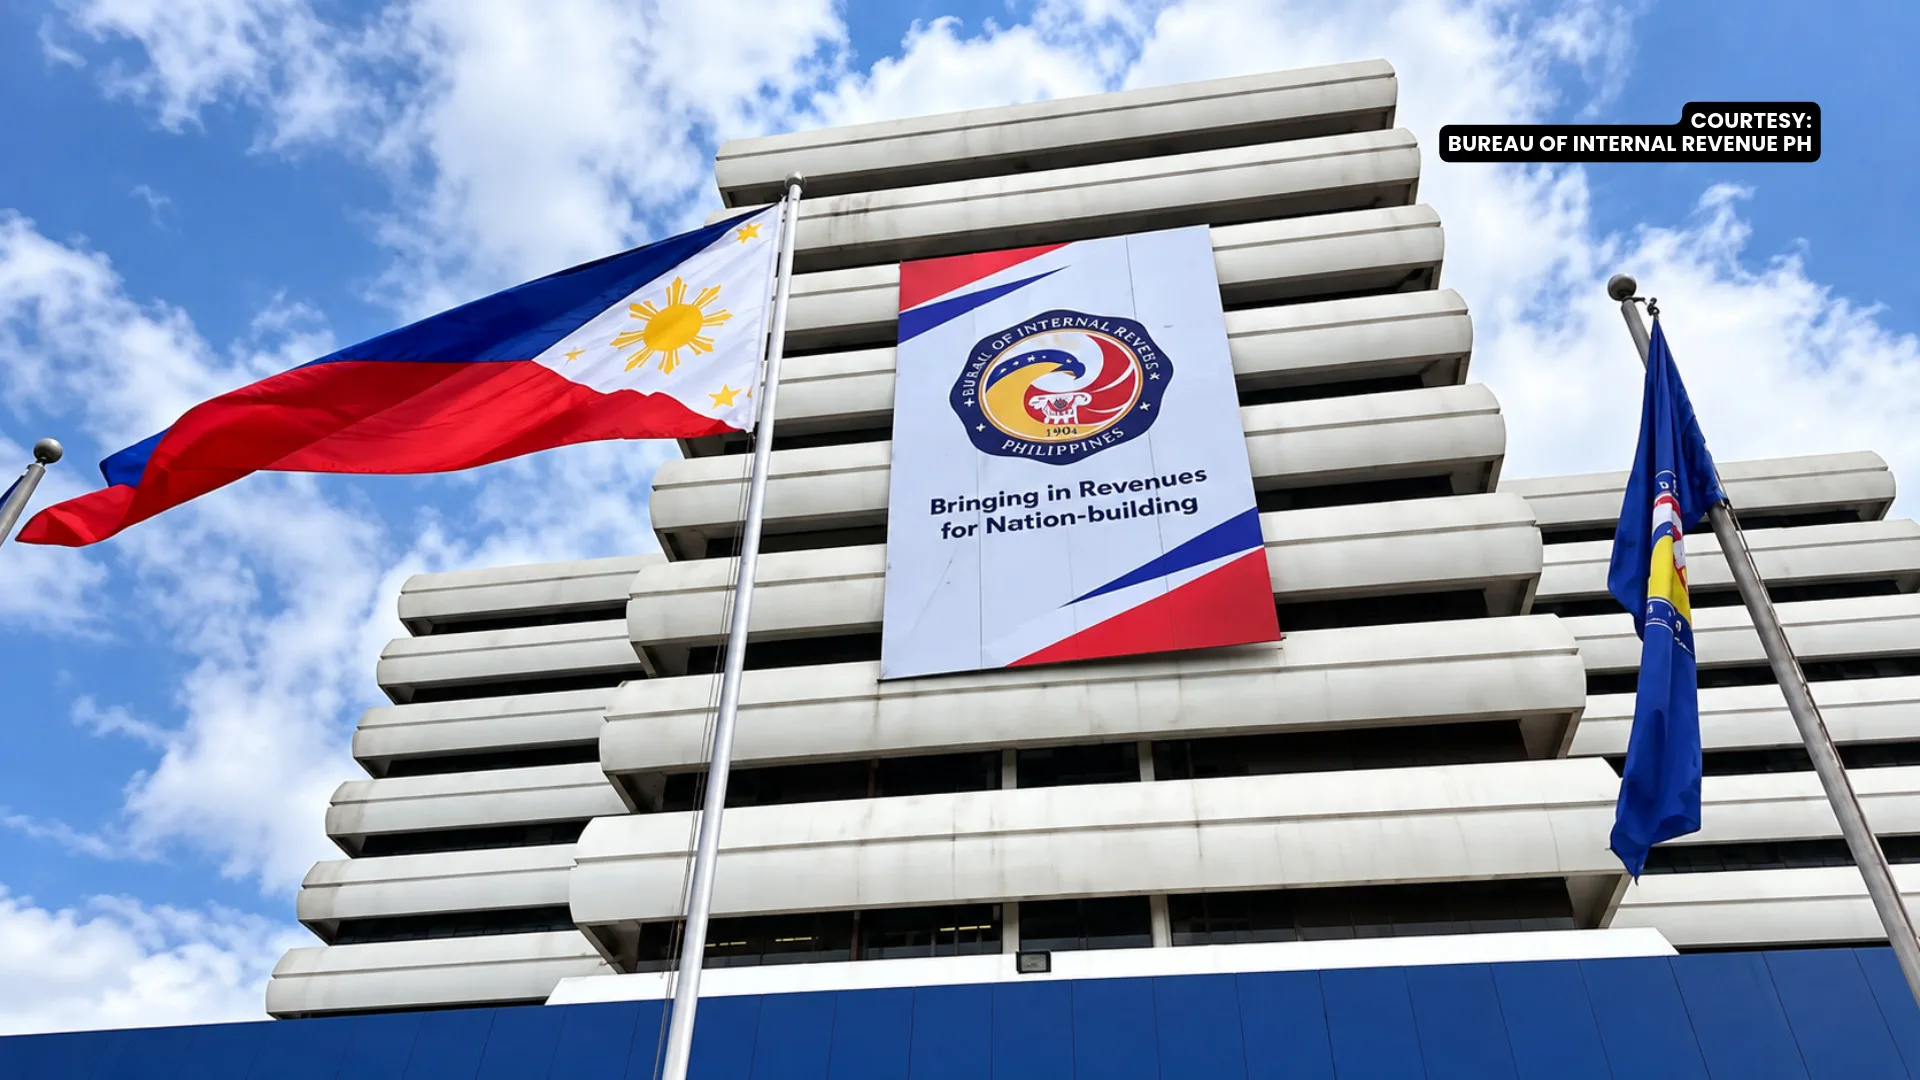
The Bureau of Internal Revenue (BIR) is investigating an alleged data leak involving information reportedly linked to the agency, in coordination with the Department of Information and Communications Technology (DICT) and anti-cybercrime authorities.
In an advisory, the BIR said it is working with the DICT, its attached agencies the National Computer Emergency Response Team (NCERT) and Cybercrime Investigation and Coordinating Center (CICC), as well as the Philippine National Police Anti-Cybercrime Group.
The alleged incident reportedly occurred on Friday, November 7.
“The Bureau of Internal Revenue is aware of reports circulating online… regarding an alleged leak involving data claimed to be associated with the agency,” the advisory read.
The BIR did not disclose the possible extent of the leak or the type of information that may have been compromised.
“We wish to inform the public that these claims are being treated with utmost urgency and priority,” the advisory also added.
The bureau also said it is strengthening its security measures while the investigation is ongoing.
On September 8, the BIR website experienced what the agency described as a “brief defacement incident.” Technical teams from the BIR and DICT promptly restored its services.
“Based on the BIR’s initial assessment, taxpayer information and core BIR systems were not affected by the incident. As a precaution, the BIR is conducting additional security checks,” the bureau also said at the time.
The reported incident came just over a week after private healthcare provider St. Luke’s Medical Center disclosed a cybersecurity incident involving its mobile application.
The National Privacy Commission (NPC) is investigating the matter after receiving a data breach notification from St. Luke’s. The commission said around 100,000 individuals may have been affected.
St. Luke’s assured the public that its critical Electronic Medical Record system containing patient records was not compromised. However, it began notifying individuals whose personal information may have been affected.